A DeFi wallet can lose money without being hacked, liquidated, or connected to an obviously malicious contract. Sometimes the failure is more ordinary: a swap is publicly visible before confirmation, a transaction executes at a worse price than expected, or a portfolio tracker quietly values a position using stale or incomplete data. The counterintuitive lesson is that portfolio visibility and transaction security are not separate conveniences. They are two views of the same risk system.
Consider a US-based user moving stablecoins across several EVM networks, supplying assets to a lending protocol, and occasionally swapping volatile tokens. The user may see a reassuring total balance while missing three different exposures: smart-contract risk in the protocol, execution risk in the next transaction, and valuation risk in the dashboard itself. A secure workflow must therefore ask not only “What do I own?” but also “Who can see my intent, how will the transaction execute, and what assumptions produced this balance?”
The portfolio is not a number
Portfolio tracking in DeFi is more difficult than checking a brokerage account because ownership and economic exposure are distributed across contracts, chains, and token standards. A wallet address may hold liquid tokens, liquidity-provider positions, lending deposits, borrowed assets, reward tokens, and claims represented by non-fungible or semi-fungible positions. The visible wallet balance is only one layer of the portfolio.
A useful mental model separates three questions. First, what assets or claims does the address control? Second, what are those claims worth under current market conditions? Third, what can go wrong before the owner can convert them back into usable funds? The first question is accounting. The second is valuation. The third is risk management. A tracker that answers only the first two can still give a dangerously incomplete picture.
Valuation is especially fragile in DeFi. A token may have a quoted market price but limited liquidity. A lending position may be worth less than its displayed collateral value if withdrawal is delayed or the market moves sharply. A liquidity position can gain fees while suffering impermanent loss. A cross-chain portfolio view may also double-count bridged representations or fail to identify that assets are locked in a contract with unusual exit conditions.
This does not make tracking useless. It changes what a good tracker should do. The goal is not false precision, such as presenting a single dollar figure as if it were guaranteed cash. The goal is to expose assumptions: which chain was inspected, which contracts were recognized, how prices were sourced, and whether the position is liquid, encumbered, or dependent on a protocol continuing to function.
MEV protection begins before the transaction is sent
Maximal extractable value, commonly called MEV, is the value that block producers and specialized searchers can capture by reordering, inserting, or selectively excluding transactions. A public transaction waiting for confirmation can reveal a profitable opportunity. In a decentralized exchange, that may allow another participant to trade before the user, trade after the user, or surround the transaction with both actions. The result can be worse execution even when the user followed the protocol’s normal interface.
The popular explanation is “bots steal your trade,” but that is too broad. MEV is not one attack and not every unfavorable execution is malicious. Price movement, thin liquidity, a wide user-selected tolerance, and ordinary arbitrage can produce similar outcomes. The practical distinction is whether the transaction’s information and ordering create avoidable extraction. Protection therefore depends on both routing infrastructure and user settings.
Private transaction submission can reduce the period during which pending transaction details are exposed to the general public mempool. Slippage limits can constrain how far execution may move from the user’s expectation. Better routing can split an order across venues or choose a path with deeper liquidity. None of these tools is absolute. A private route may have different trust assumptions, limited availability, or its own failure modes. A tight slippage limit can protect price but also increase the chance that a transaction fails during volatility.
The important connection to portfolio tracking is timing. A tracker describes the portfolio before and after a transaction; MEV protection influences whether the transition between those states is economically acceptable. If a dashboard shows that a user owns $10,000 of a token but ignores the cost of exiting a shallow market, it is reporting an inventory value rather than a realizable value. For active DeFi users, execution quality is part of portfolio performance.
DeFi protocols create different kinds of exposure
Protocols should not be compared only by headline yield. A lending market, automated market maker, liquid-staking system, and yield aggregator each transform risk in different ways. Lending introduces utilization, interest-rate, liquidation, oracle, and contract risks. Automated market making introduces inventory imbalance and liquidity sensitivity. Yield aggregators add another layer of strategy and contract dependencies. The displayed annual percentage rate is an output of these conditions, not a permanent property of the asset.
That matters when portfolio trackers group positions under broad labels such as “stablecoins,” “yield,” or “cash equivalent.” Two dollar-pegged assets can have different redemption mechanisms, collateral structures, and liquidity profiles. Two lending positions can have different liquidation thresholds and oracle dependencies. A well-designed review process should preserve the protocol context instead of flattening every position into a ticker symbol.
There is also a boundary condition that users often miss: simulations are strongest at detecting what a transaction is likely to do under a particular state, but they cannot guarantee the state will remain unchanged until inclusion. A swap may simulate successfully while another transaction changes pool reserves moments later. A contract may behave differently under an unexpected token transfer or a new market condition. Simulation is therefore a powerful pre-flight check, not a replacement for economic judgment.
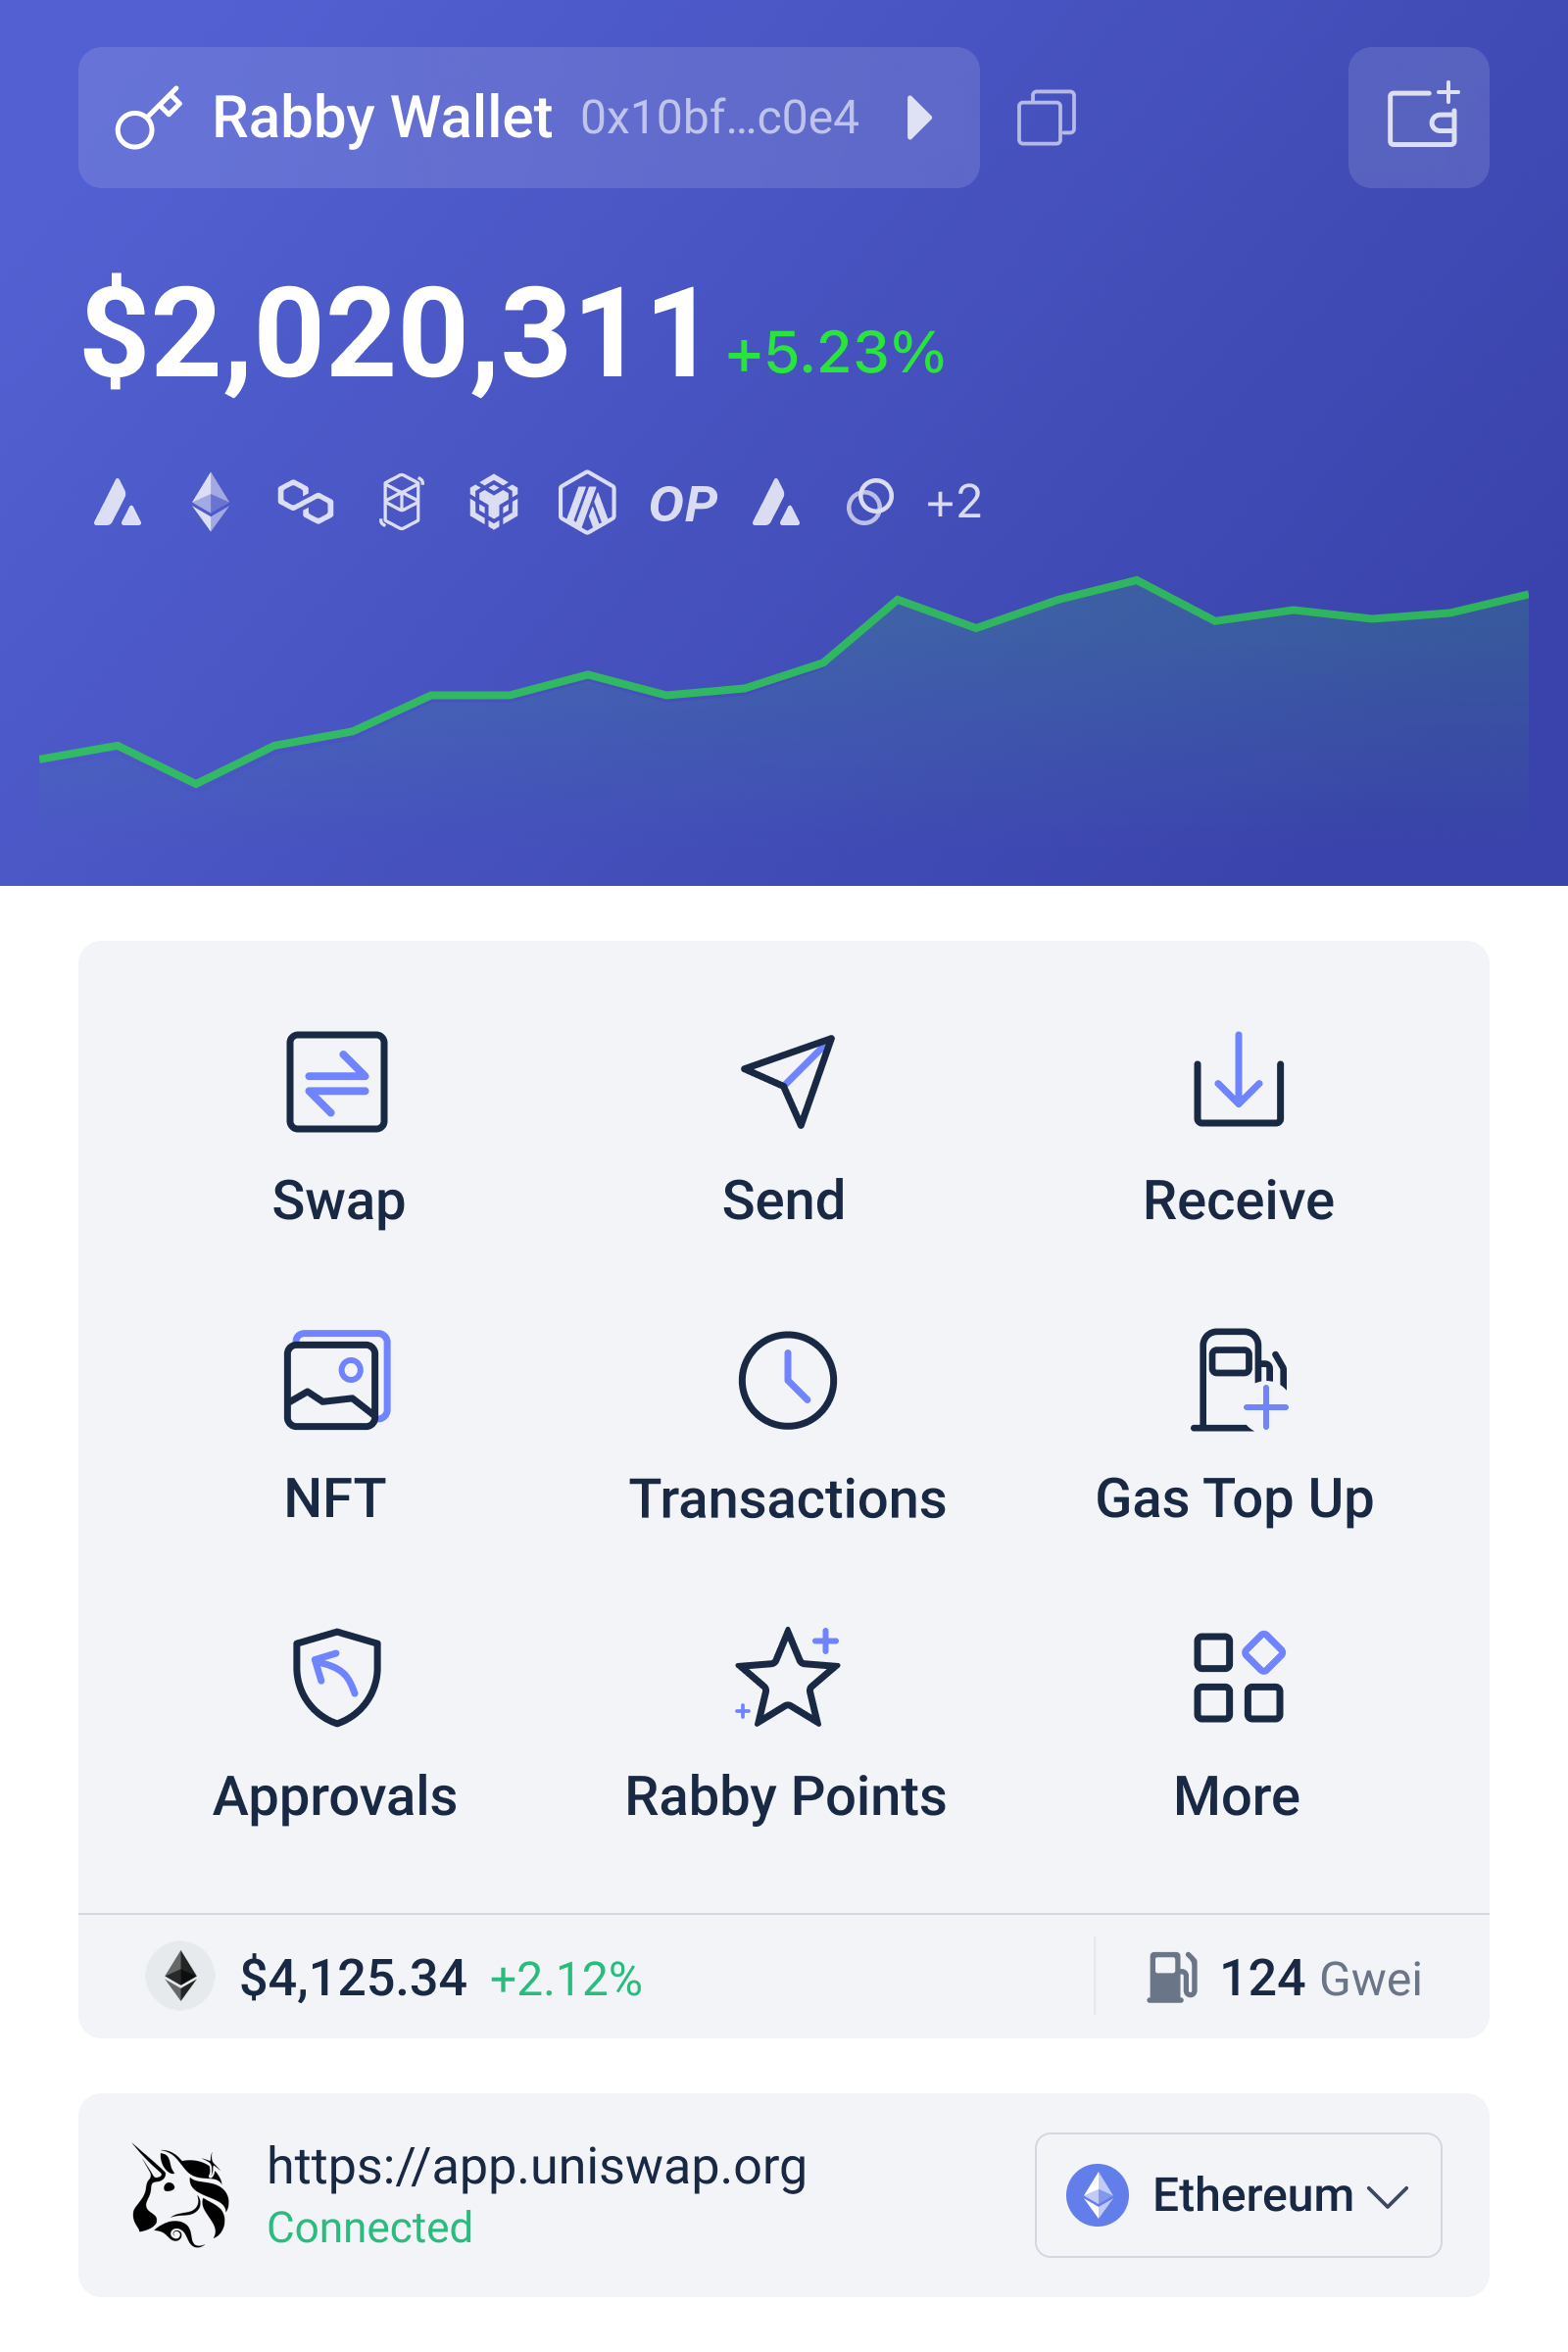
For users who want an advanced EVM workflow, rabby wallet can be useful as part of that review layer because transaction simulation and security-oriented warnings help translate contract calls into consequences before signing. The sensible interpretation is not that a wallet makes DeFi risk disappear. Rather, it can reduce avoidable errors by giving the user more information at the decision point.
A practical security framework for DeFi users
Before approving a transaction, separate the review into four questions. What is leaving the wallet? What is expected to arrive? Which contracts and permissions are involved? What is the worst plausible outcome if the market or protocol state changes? This sequence catches different classes of mistakes. A familiar token name may conceal an unlimited approval. A transaction described as a swap may include a route through several contracts. A staking action may create a derivative token whose value depends on a secondary market.
For portfolio monitoring, classify positions by liquidity and dependency rather than by token symbol alone. Immediately spendable assets are different from assets locked in a contract. Assets with deep markets are different from assets whose displayed value depends on a small pool. A position relying on one oracle, bridge, or upgradeable contract should not be treated as equivalent to a self-custodied native asset. This classification is more decision-useful than a single risk score because it shows what kind of failure the user would face.
Approvals deserve special attention. An approval is not the transfer itself; it is permission for a contract or spender to move tokens later, subject to the allowance. Revoking unnecessary permissions can reduce the blast radius of a compromised or malicious contract, although revocation itself requires a transaction and may involve network fees. Users should also distinguish a failed transaction from a successful but harmful one. Failure may cost gas, while a successful transaction can authorize a transfer or move assets irreversibly.
MEV protection should be calibrated to the trade. For a small, highly liquid swap, complex privacy infrastructure may provide little incremental benefit. For a large order in a thin pool, execution method, route, slippage tolerance, and transaction visibility matter much more. The right question is not “Am I protected?” but “Which risk is material for this transaction, and which control actually addresses it?”
What to watch as wallet intelligence improves
Recent positioning around EVM wallets emphasizes broad chain coverage, speed, and security across on-chain activity. If that direction continues, the most valuable progress will not be another list of supported networks. It will be better interpretation: clearer distinctions between owned assets and protocol claims, more realistic liquidation and exit estimates, and warnings that connect a transaction to the user’s existing exposure.
One conditional scenario is especially important. If wallets can combine portfolio state, transaction simulation, contract permissions, and execution conditions without overwhelming users, they may become risk-management interfaces rather than simple signing tools. That would help users detect concentration, hidden dependencies, and repeated approval exposure before those risks become losses. The unresolved challenge is that more automation can also create more false confidence. A warning system that produces too many alerts may be ignored; one that compresses uncertainty into a green checkmark may be misleading.
The durable principle is simple but demanding: visibility is not safety, and simulation is not certainty. Portfolio tracking tells you what the system believes you hold. MEV-aware execution helps determine what you actually receive. Protocol analysis explains what stands between the wallet and that outcome. DeFi becomes more manageable when these layers are reviewed together rather than treated as separate features.
Frequently asked questions
Does portfolio tracking protect assets from MEV?
No. Tracking improves awareness of balances, positions, and changes, but it does not control transaction ordering. MEV protection requires measures such as appropriate routing, sensible slippage limits, and, where suitable, private transaction submission.
Can transaction simulation guarantee that a DeFi transaction is safe?
No. Simulation can reveal expected transfers, approvals, contract interactions, and likely outcomes under a particular state. It cannot guarantee that market conditions, liquidity, contract behavior, or transaction ordering will remain unchanged before confirmation.
What is the most useful portfolio metric beyond total dollar value?
Liquidity-adjusted exposure is often more informative. Ask how quickly each position can be exited, what market depth supports its quoted price, and which protocols, oracles, bridges, and permissions the position depends on. That turns a headline balance into a more realistic risk picture.